




Information Security
Information Security
Information Security Policy
Information Security Policy
Information Security Policy
-
1.Purpose
The purpose of this policy is to ensure the confidentiality, integrity, and availability of all information assets owned or used by the Company and to appropriately manage information security risks. The Company shall establish an Information Security Management System (ISMS) based on ISO/IEC 27001 and continually improve it. -
2.Scope
This policy applies to all information assets related to the Company’s business activities. It applies to all officers, employees, contract employees, temporary staff, and any other personnel who handle information in the course of their duties. -
3.Basic Principles of Information Security
-
(1)Protection of Information Assets
The Company shall identify its information assets and implement appropriate controls based on risk assessment. -
(2)Compliance with Laws and Contractual Requirements
The Company shall comply with all applicable laws, regulations, and contractual requirements related to information security. -
(3)Information Security Risk Management
In accordance with ISO/IEC 27001, the Company shall regularly assess information security risks and implement appropriate risk treatment measures. -
(4)Access Control and Information Handling
Access to information shall be restricted to personnel who require it for business purposes.
Information acquisition, use, storage, and disposal shall be managed appropriately. -
(5)Incident Response
The Company shall work to prevent information security incidents.
In the event of an incident, the Company shall respond promptly and appropriately to minimize impact and prevent recurrence. -
(6)Education, Training, and Continual Improvement
The Company shall provide information security education to all employees and continually improve the ISMS through internal audits and management reviews.
-
(1)Protection of Information Assets
-
4.Roles and Responsibilities
Top management is responsible for establishing and maintaining the ISMS and for providing the necessary resources.
The Information Security Manager shall oversee the implementation and administration of this policy.
All employees and related personnel shall comply with this policy and associated regulations. -
5.Review of the Policy
This policy shall be reviewed at least once a year, or as necessary in response to changes in business activities, laws, or ISO/IEC 27001 requirements.
Date of Establishment: January 23, 2026
Name of Representative: Keiichi Yoshioka, President & CEO
Company Name: Nisshinbo Micro Devices Inc.
Information Security Management System Status
Information Security Management System Status
Information Security Management System Certificate (C841666)
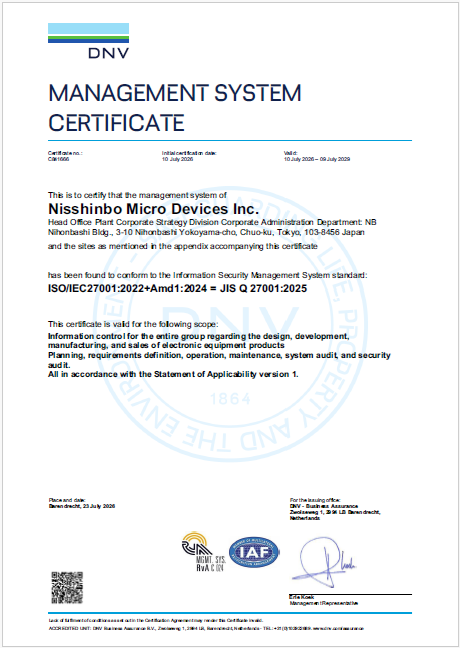
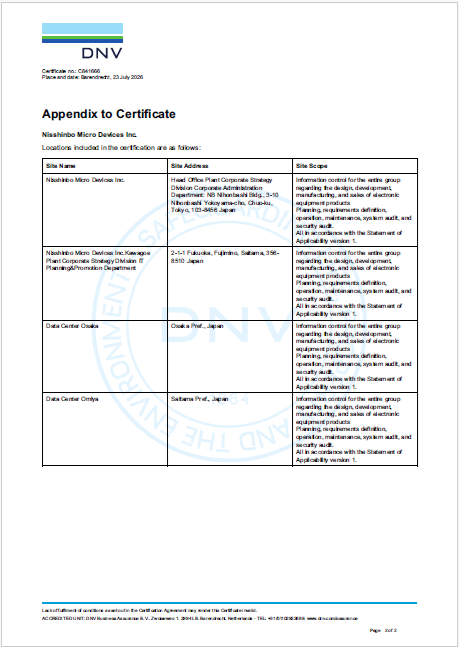
| Registration Date | July 10, 2026 |
|---|---|
| Expiry Date | July 9, 2029 |
| Certificate Number | C841666 |
| Certification Body | DNV - Business Assurance |
| Scope of Certification |
Information control for the entire group regarding the design, development, manufacturing, and sales of electronic equipment products Planning, requirements definition, operation, maintenance, system audit, and security audit. All in accordance with the Statement of Applicability version 1. |
Information Security Management System Certificate (C841667)
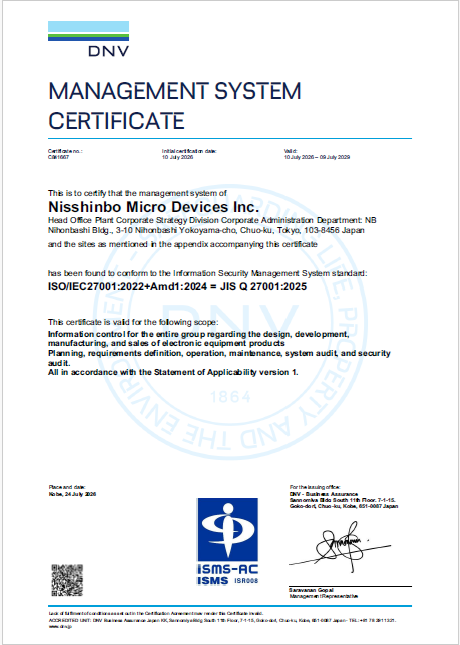
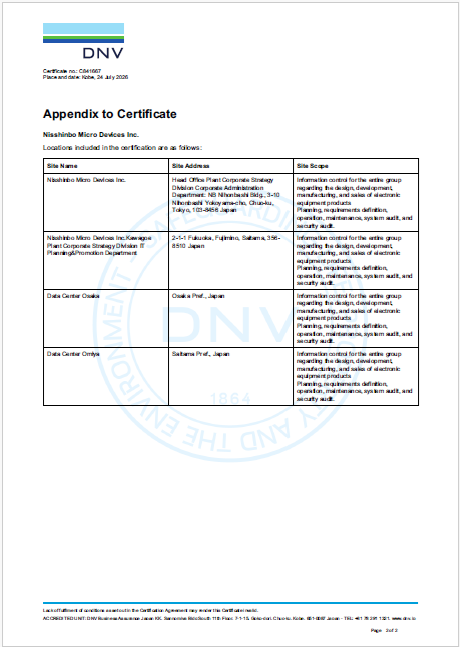
| Registration Date | July 10, 2026 |
|---|---|
| Expiry Date | July 9, 2029 |
| Certificate Number | C841667 |
| Certification Body | DNV - Business Assurance |
| Scope of Certification |
Information control for the entire group regarding the design, development, manufacturing, and sales of electronic equipment products Planning, requirements definition, operation, maintenance, system audit, and security audit. All in accordance with the Statement of Applicability version 1. |